


Enterprise Threat Detection and Response
Rapid threat detection and 24/7 incident response.
PBXGlobal delivers incident response services in New York that help businesses detect threats early, contain attacks fast, and recover with confidence. Our team combines cyber threat intelligence, proactive monitoring, and structured response strategies to help organizations stay protected and resilient.


Our Threat Intelligence and Incident Response Capabilities
Our capabilities cover every phase of the threat lifecycle, from early detection to full recovery, giving your organization a clear, coordinated path through any security event.

Managed Incident Response Services
Our managed incident response service provides businesses with dedicated security experts who take immediate ownership of any active threat. From initial triage to full resolution, every step is documented, coordinated, and executed without delay.

Threat Intelligence and Monitoring
Our managed incident response service provides businesses with dedicated security experts who take immediate ownership of any active threat. From initial triage to full resolution, every step is documented, coordinated, and executed without delay.

Ransomware Incident Response
Ransomware demands fast action. Our ransomware incident response services in NYC include immediate isolation of affected systems, forensic analysis, decryption support where applicable, and a structured recovery plan that minimizes downtime and data loss.

Threat Detection and Alerting
Our detection capabilities are built around behavioral analytics and real-time correlation of security events. High-fidelity alerts reduce noise and ensure your team focuses only on threats that require immediate attention and action.

Incident Containment and Remediation
Once a threat is confirmed, containment begins immediately. We isolate compromised assets, eliminate attacker footholds, and apply targeted remediation steps that restore integrity across your environment efficiently and thoroughly.
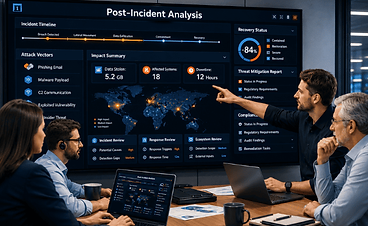
Post-Incident Analysis and Reporting
After every incident, a detailed analysis identifies root causes, attack vectors, and gaps in existing controls. These findings translate into clear, actionable recommendations that strengthen your security posture going forward.
Beneficial Features of Our Threat Intelligence and Incident Response
Security teams already managing daily operations rarely have the bandwidth to handle a major incident effectively. That gap is exactly where our services deliver the most value, stepping in with structure, speed, and expertise that internal teams often cannot mobilize alone. The following are key features of our threat intelligence and incident response services:
Security Operations Center (SOC) Support
Our SOC security services in Long Island provide continuous oversight of your environment. Dedicated analysts monitor alerts, investigate anomalies, and escalate confirmed threats with full context, so your team receives clarity, not just notifications.
24/7 Threat Monitoring and Escalation
Our around-the-clock monitoring ensures that no threat goes undetected during off-hours, weekends, or holidays. Escalation protocols are immediate and structured, with no delays between detection and response. targeting your business.
Rapid Response Workflows
Our response workflows are pre-built and tested, which means when an incident occurs, there is no scrambling to figure out next steps. Response begins within minutes, reducing attacker dwell time and limiting the blast radius of any security event.
Actionable Threat Intelligence Integration
Threat data is only useful when it helps to make decisions. We integrate cyber threat intelligence directly into your security operations, ensuring alerts are enriched with context that helps analysts act faster and with greater accuracy.
Regulatory and Compliance Alignment
Every incident response engagement is conducted with documentation standards that support regulatory requirements. Whether you operate under HIPAA, PCI-DSS, or other frameworks, our reporting gives you the evidence trail you need.